A collection of redacted award notifications and security report records, with public write-ups grounded in the accompanying screenshot evidence.
01 / AWARD NOTIFICATIONREDACTED DUE TO NDA
Confidential report · $20,000 award
$20,000 awarded
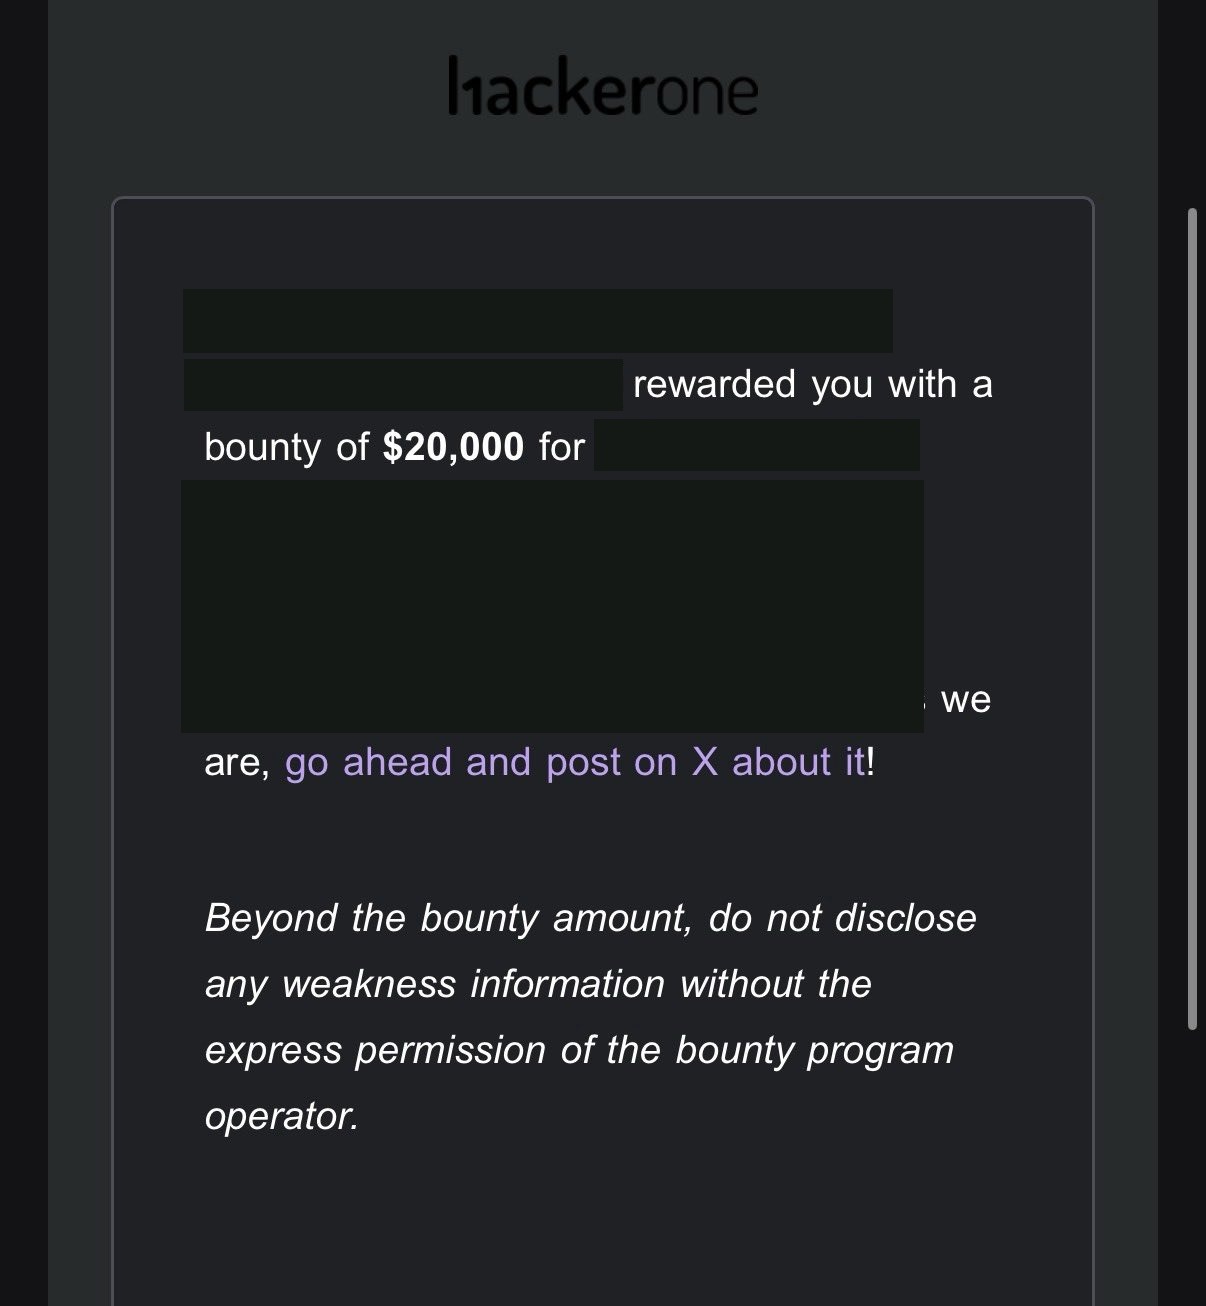
A redacted HackerOne notification documenting a $20,000 bounty award. Vulnerability details remain withheld.
Read write-up & view evidence
Public record
The supplied notification states that a program rewarded the report with a $20,000 bounty. This write-up preserves that award acknowledgment while withholding the program, report title, affected assets, and technical weakness information.
Disclosure boundary
The notification distinguishes disclosure of the bounty amount from disclosure of weakness information. Accordingly, this public entry contains no vulnerability classification, affected feature, reproduction steps, payloads, or impact details. Those sections are redacted due to NDA.
What the evidence establishes
The screenshot documents an award notification. It is not a bank receipt, a remediation report, or evidence of the date a fix reached production. No additional payout status or remediation claim is inferred.
Outcome and evidence handling
The public outcome is the documented award. Additional opaque redactions were applied to the exported screenshot, and image metadata was removed. The original correspondence is not hosted on this website.
Screenshot evidence
Award notification showing $20,000. Program identity and weakness information are permanently obscured. Open full image ↗
02 / AWARD NOTIFICATIONREDACTED DUE TO NDA
Zero-click report · $10,000 award
$10,000 awarded
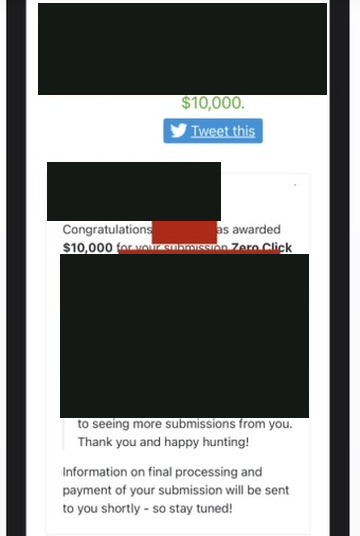
A redacted notification recognizing a zero-click report with a $10,000 award and describing payment processing as a later step.
Read write-up & view evidence
Public record
The screenshot contains an award message stating $10,000 and a congratulations message for the zero-click submission. Identifying content is redacted. The remaining correspondence mentions that further information about final processing and payment will follow.
Technical details
The target, affected component, discovery workflow, reproduction steps, and technical impact are redacted due to NDA. This public record intentionally does not reconstruct the hidden report from fragments of the notification.
Award versus payment
An award notification and a completed payment are different records. This entry describes the former; the screenshot alone does not establish that funds were received or when payment completed.
Relationship to other reports
This notification is presented separately as an evidence item. It has not been matched to the other report screenshots, and the site does not add the award amounts into a lifetime earnings total or claim that every screenshot is a separate paid bounty.
Screenshot evidence
The visible award amount is $10,000. Recipient, program, and report details are obscured. Open full image ↗
03 / REPORT RECORDREDACTED DUE TO NDA
Object authorization · unauthorized editing
Critical label shown
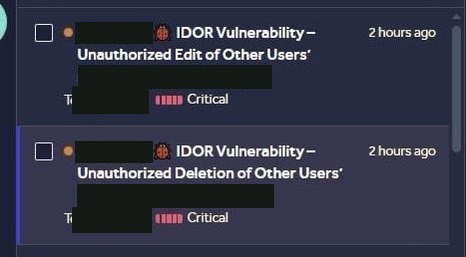
A report-list entry describing unauthorized editing of another user’s records through an object identifier.
Read write-up & view evidence
Reported issue
The visible report title describes an insecure direct object reference (IDOR) involving unauthorized editing of another user’s records. The security property at issue is whether one account can modify an object that belongs to another account.
Evidence and scope
The screenshot shows an edit report and a separate deletion report, each with a Critical label. This entry covers the editing report only. The screenshot is a report-list view, not a reproduction transcript or a confirmation of program acceptance.
Potential impact described by the report
Unauthorized modification would affect the integrity of another account’s data. The public evidence does not establish the number of affected users, the fields that could be changed, the prerequisites, or whether the Critical label was assigned or accepted by the program.
NDA redactions and outcome
The program, recipient, report identifier, object parameter, endpoint, requests, and proof-of-concept details are withheld. No award, remediation confirmation, or final resolution is visible in this evidence; those outcomes are not claimed.
Screenshot evidence
Shared evidence for two separate report-list entries: unauthorized editing and unauthorized deletion. Report IDs, recipient, and parameter name are obscured. Open full image ↗
04 / TRIAGE UPDATESREDACTED DUE TO NDA
Reflected XSS · classification and priority review
P3 → P5 shown
Two notifications for the same reflected XSS report, combined into one record of its classification and priority changes.
Read write-up & view evidence
Reported issue
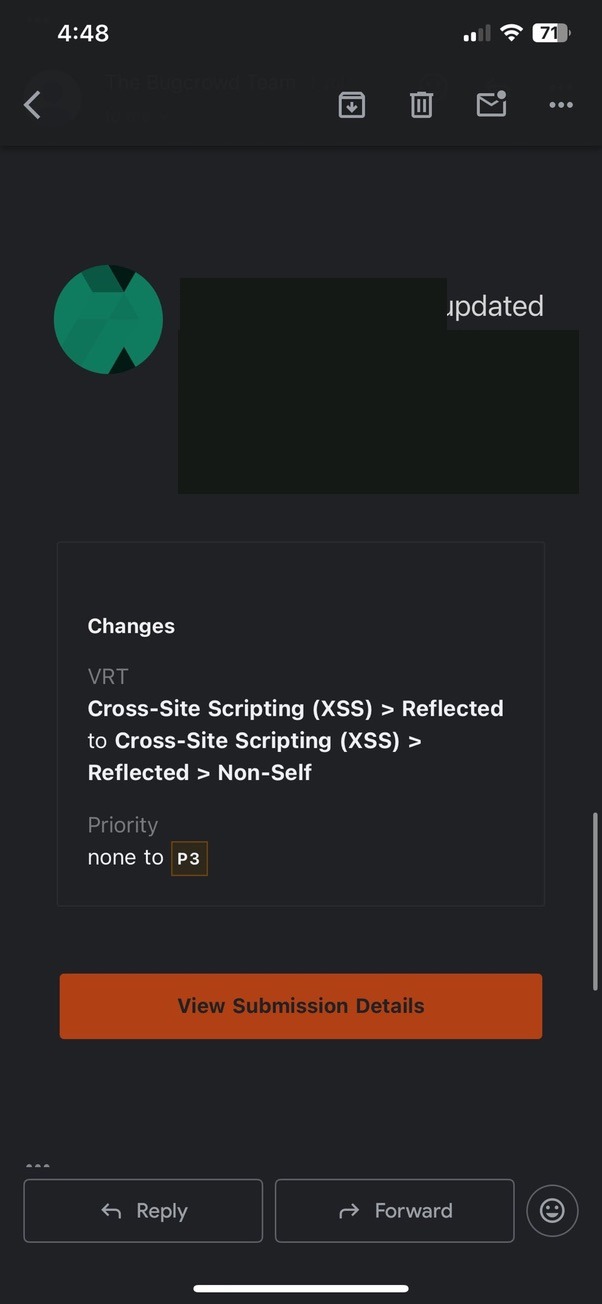
The original notification titles identify the same reflected cross-site scripting report. The target-specific title and parameter details are withheld in this public version. The visible classification change describes reflected, non-self XSS.
Triage history
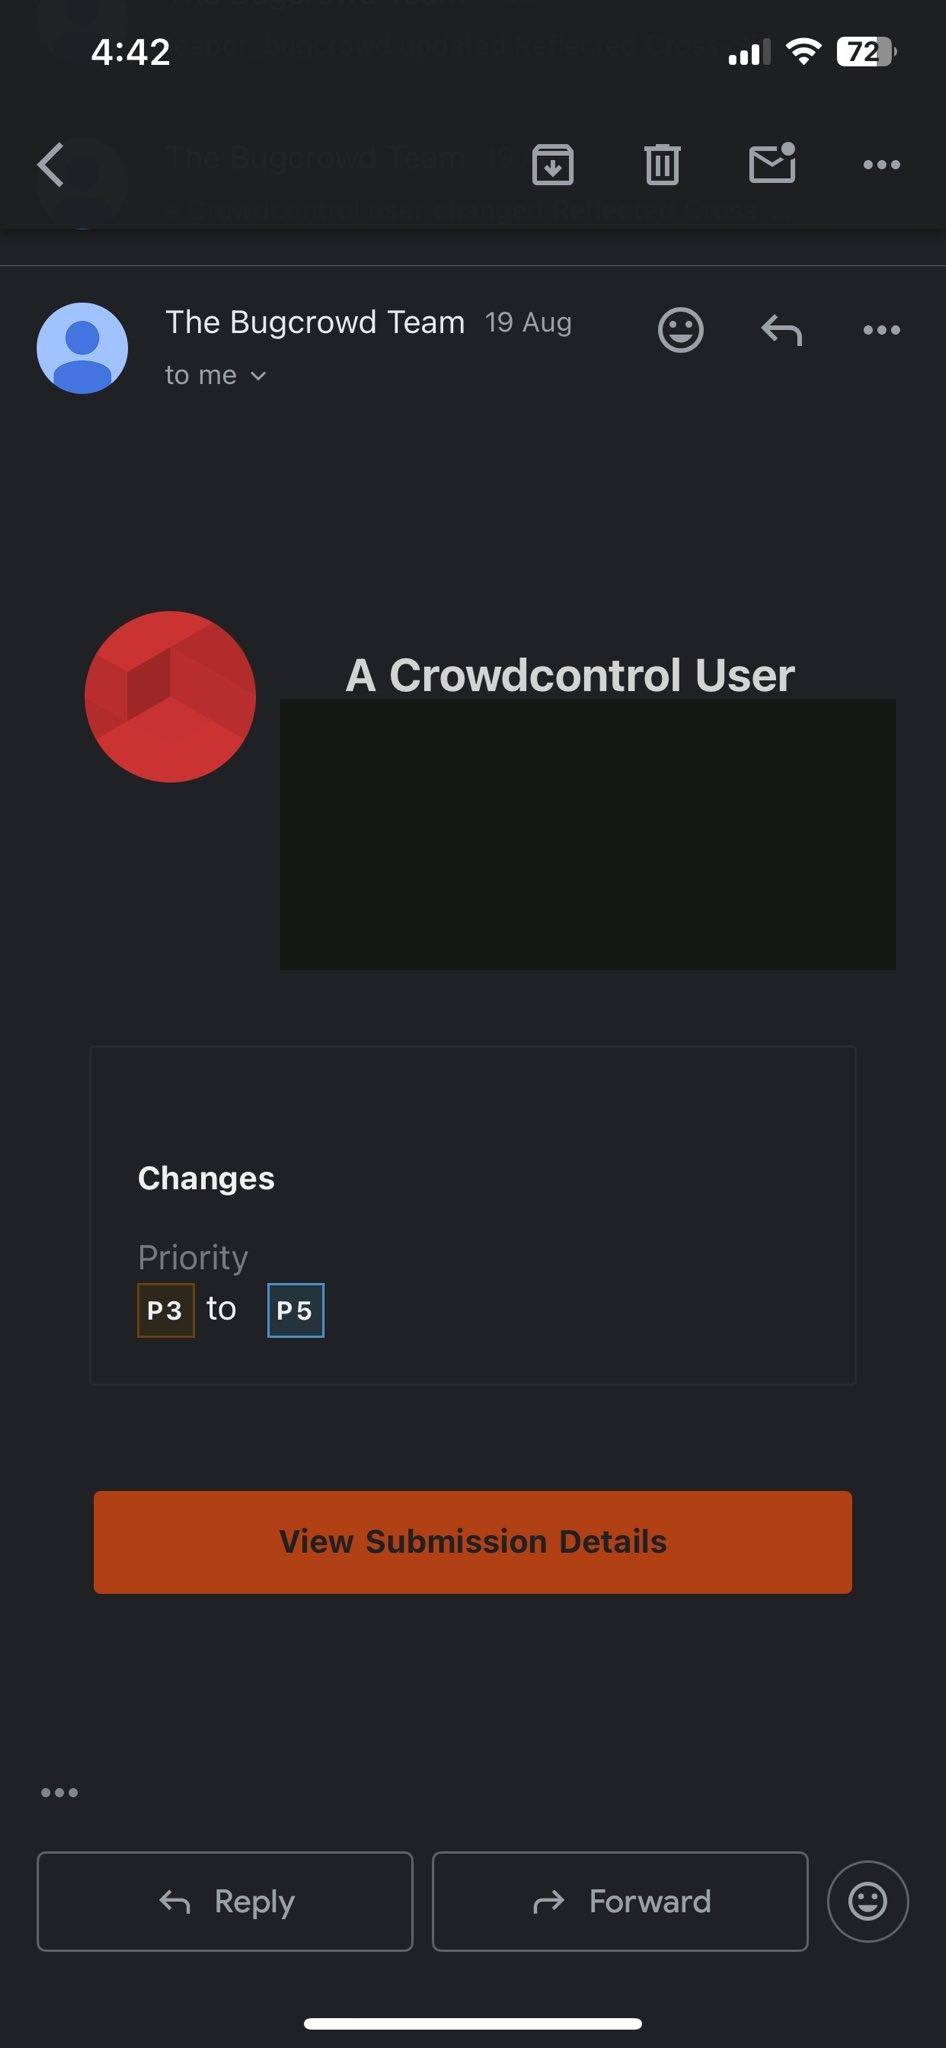
One notification changes the classification from reflected XSS to reflected, non-self XSS and changes priority from none to P3. The other changes priority from P3 to P5. These are updates to one report, not two independent findings.
Interpreting the result
The public record includes both updates rather than presenting only the higher priority. The latest priority transition shown is P3 to P5. The screenshots do not explain the reviewer’s reasoning, establish the current live status, or show an award.
NDA redactions
Program and product identifiers, reviewer identity, the affected input, URL, payload, browser behavior, and reproduction steps are withheld. The screenshots demonstrate the review history; they do not serve as a public exploit demonstration or proof of remediation.
Screenshot evidence
Classification update to Reflected → Non-Self, with priority changing from none to P3. Target and reviewer identity are obscured. Open full image ↗A subsequent priority update shows P3 changing to P5. The target-specific title is obscured. Open full image ↗
05 / REPORT RECORDREDACTED DUE TO NDA
Account takeover · triaged report
P1 · Triaged · In progress
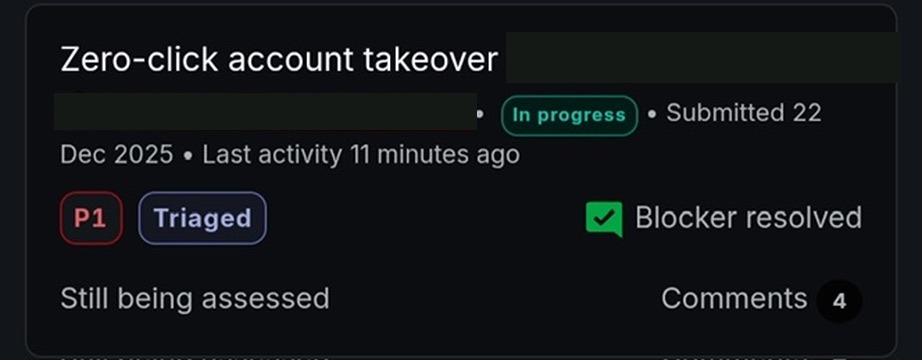
A report status screenshot showing a zero-click account-takeover title, P1 priority, and a triaged but ongoing assessment.
Read write-up & view evidence
Reported issue
The visible report title describes zero-click account takeover. The mechanism and identifying details are redacted due to NDA. The title is recorded as the report’s stated issue; the public screenshot does not contain the technical demonstration.
Assessment shown
The screenshot shows a submission date of 22 December 2025, P1 priority, Triaged status, and In progress. It also says Still being assessed. These labels describe the captured record and are not represented as a live status feed.
Meaning of the blocker update
The green Blocker resolved indicator is preserved as part of the evidence. Resolving a workflow blocker does not, by itself, establish that the underlying vulnerability was fixed or that a bounty was awarded. No such conclusion is drawn here.
Public disclosure limit
Account identifiers, program identity, the mechanism, technical prerequisites, payloads, and reproduction sequence are withheld. The screenshot supports the report’s triage state but does not document payment, final severity acceptance, or a completed remediation.
Screenshot evidence
P1, Triaged, In progress, Still being assessed, and Blocker resolved are visible. The program and mechanism are obscured. Open full image ↗
06 / ASSESSMENT RECORDREDACTED DUE TO NDA
Business logic · high-severity assessment
CVSS 8.2 · Under review
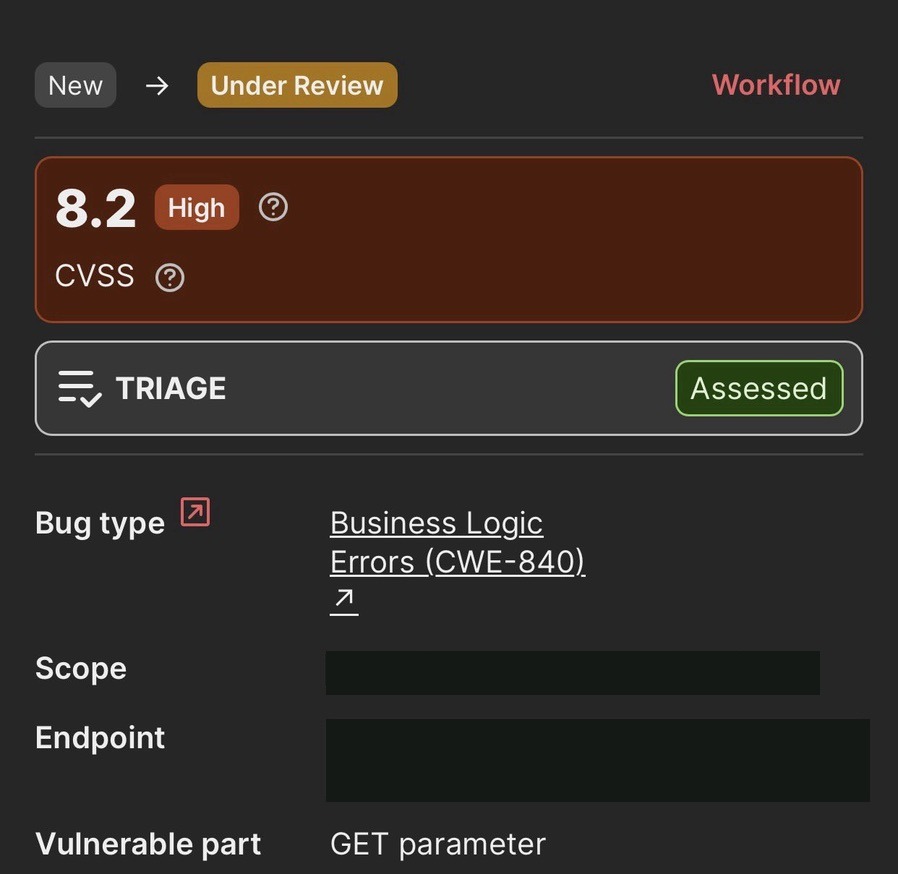
A redacted assessment showing a business-logic classification, a High score of 8.2, and an Under Review workflow state.
Read write-up & view evidence
Visible classification
The screenshot classifies the report as Business Logic Errors (CWE-840). It shows a CVSS score of 8.2 with a High label and identifies a GET parameter as the vulnerable part. The parameter name, scope, and endpoint are withheld.
Review state
The workflow shows New transitioning to Under Review, while the triage panel says Assessed. These are the states visible in the capture; they do not prove that a fix was deployed, a report was publicly disclosed, or an award was paid.
Limits of the assessment
No CVSS vector, affected business workflow, reproduction sequence, or impact narrative is included in the supplied image. This write-up therefore does not infer specific privileges, financial loss, account access, or exploit conditions from the numerical score alone.
NDA redactions
The target domain, endpoint, request parameters, sensitive data, and technical proof are redacted due to NDA. The public evidence is an assessment summary, not a complete technical report. No final resolution or bounty amount is visible.
Screenshot evidence
CVSS 8.2 High, Assessed triage, Business Logic Errors (CWE-840), and Under Review are visible. Scope and endpoint are obscured. Open full image ↗
07 / RELATED SUBMISSIONSREDACTED DUE TO NDA
Azure App Service · subdomain takeover submissions
P3 · New · In progress
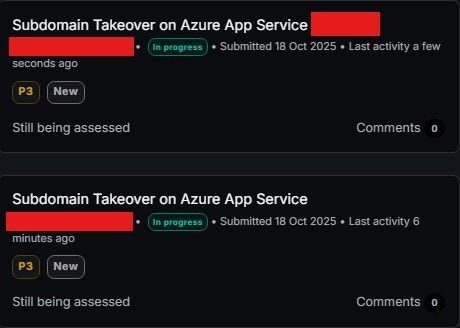
Two similar subdomain-takeover submissions grouped into one write-up because their redacted assets cannot be distinguished publicly.
Read write-up & view evidence
Reported issue
Both visible titles describe subdomain takeover on Azure App Service. The affected hostnames and program identities are redacted. The image does not include DNS records, a service response, an asset claim, or proof of control.
Grouping the evidence
The screenshot contains two similar submissions dated 18 October 2025. Because the identifying content is obscured, it is not possible to establish from this image whether they affect different assets or overlap. They are grouped rather than counted as two distinct confirmed vulnerabilities.
Assessment state
Both entries show P3 and New, with In progress and Still being assessed indicators. These labels record the submission state at capture time. They do not establish program validation, completed remediation, or a bounty award.
Disclosure boundary
Target domains, DNS configuration, resource identifiers, verification details, and reproduction instructions are redacted due to NDA. No live asset is identified and no takeover instructions are published in this portfolio entry.
Screenshot evidence
Two Azure App Service subdomain-takeover entries, each showing P3, New, and Still being assessed. Target identities are already redacted. Open full image ↗
08 / BOUNTY & TRIAGE RECORDREDACTED DUE TO NDA
IDOR report · $500 bounty
Medium (5.3) · Triaged (Open) · $500
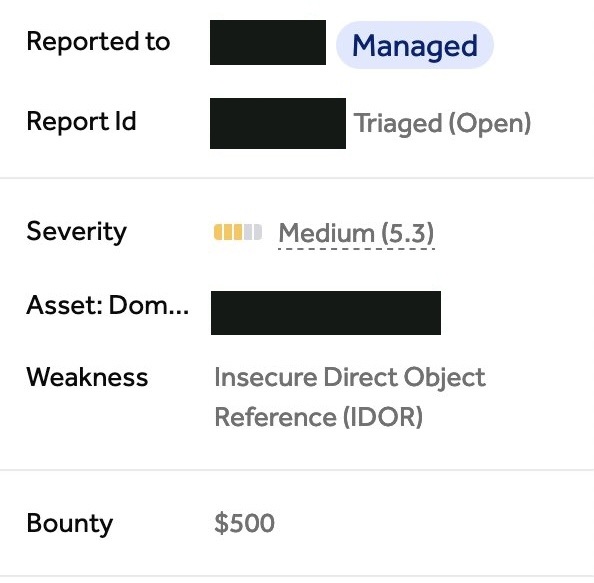
A redacted report summary documenting an insecure direct object reference finding, a $500 bounty, and an open triage state.
Read write-up & view evidence
Public record
The supplied screenshot identifies the weakness as Insecure Direct Object Reference (IDOR). It displays Medium severity with a score of 5.3, a bounty value of $500, and the status Triaged (Open). These fields are preserved together so the public record shows both the recognition and the unresolved workflow state at capture time.
Reported security boundary
The visible classification concerns object-level authorization: whether access to a referenced object is restricted to an authorized user. The screenshot does not identify the operation involved, the object type, the required privileges, or the scope of affected data. Those details are not inferred from the classification alone.
Outcome and limits
The report record documents a $500 bounty. It does not show a payment receipt, a remediation confirmation, or a closed report state. The Medium (5.3) rating is the value visible in the screenshot; a scoring vector and assessment rationale are not supplied.
NDA redactions
The program identity, report identifier, affected asset, endpoints, object identifiers, requests, and reproduction steps are redacted due to NDA. This screenshot is retained as evidence of the report classification, bounty field, and triage status, rather than as a public exploit demonstration. This entry is not assumed to be related to the other IDOR reports on this page.
Screenshot evidence
Report summary showing Medium (5.3), Insecure Direct Object Reference (IDOR), Triaged (Open), and a $500 bounty. The program, report ID, and asset are permanently obscured. Open full image ↗
09 / REPORT RECORDREDACTED DUE TO NDA
Remote command execution · Critical report
Critical label shown
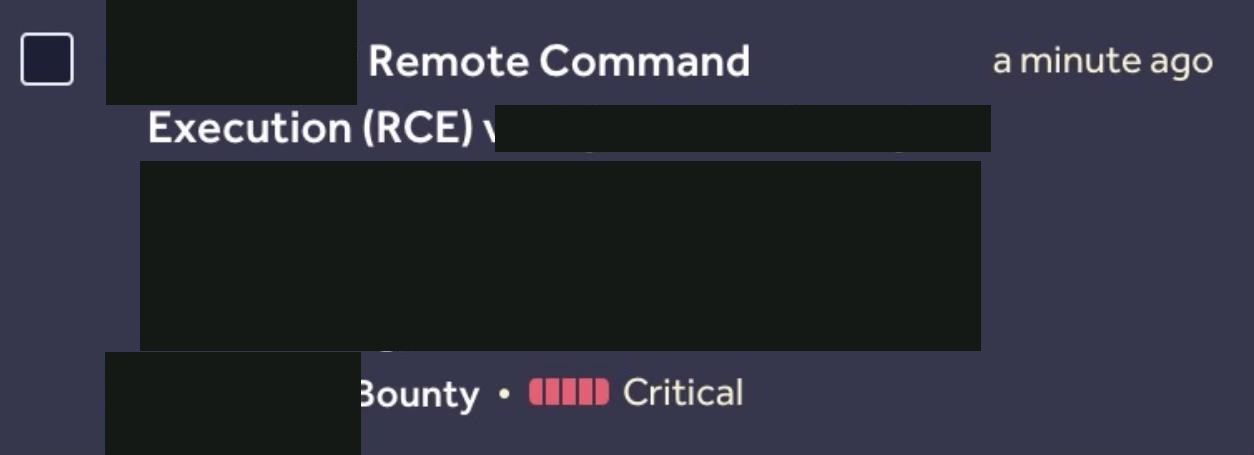
A redacted report-list entry describing remote command execution and displaying a Critical severity label. No award amount or final outcome is visible.
Read write-up & view evidence
Reported issue
The supplied report-list screenshot describes remote command execution (RCE). A Critical label is visible alongside the entry. The public write-up records the issue as reported; the screenshot itself does not contain the underlying technical proof or demonstrate that command execution occurred.
Potential impact described by the report
A report of remote command execution concerns the possibility of executing commands in an affected application environment. The supplied evidence does not establish the execution context, required access, affected versions, data exposure, or whether the behavior was independently reproduced during triage. No target-specific impact is asserted beyond the visible report title.
Evidence and status
This evidence is a report-list entry rather than an award notification or a completed remediation record. It does not show an award amount, acceptance decision, resolution status, or fix date. The Critical label is described as displayed, without assuming that it represents a final program assessment.
NDA redactions
The program and report identifiers, framework-specific details, injection mechanism, filtering-related details, payloads, endpoints, and reproduction sequence are withheld. The published image is a flattened, metadata-free copy with permanent redactions. No claim is made that this entry corresponds to either confidential award notification elsewhere on the page.
Screenshot evidence
Report-list evidence showing the remote command execution title and Critical label. Identifiers and implementation-specific details are permanently obscured. Open full image ↗
10 / AWARD NOTIFICATIONREDACTED DUE TO NDA
Confidential report · $500 bounty + $250 bonus
$500 bounty · $250 bonus
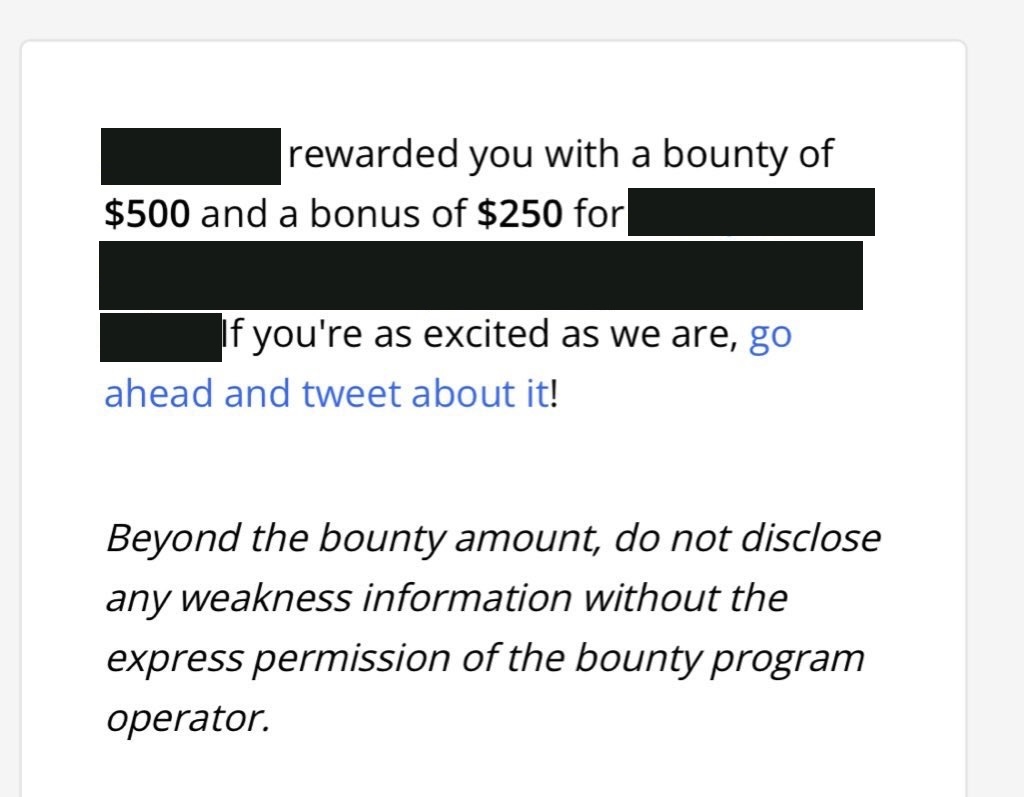
A redacted award notification documenting a $500 base bounty and a separate $250 bonus. Account and weakness details are withheld.
Read write-up & view evidence
Public record
The notification states that a report received a bounty of $500 and a bonus of $250. Both amounts are retained as separate components of the recognition. The account username and program identity are withheld from this public entry.
Disclosure boundary
The affected functionality, report title, tool-related details, request modifications, and reproduction steps are redacted due to NDA. The public write-up documents the award without reconstructing the concealed weakness from the original correspondence.
Award and payment
The screenshot is evidence of an award notification, not a payment receipt. It does not show a final remediation state, payment date, or confirmation that funds reached the recipient. Those outcomes are not claimed.
Relationship to other evidence
This notification is presented as an evidence record. Its relationship to the existing $500 IDOR entry has not been established, so it is not used to calculate a distinct-finding count or combined earnings total. The published image is a permanently redacted, metadata-free export.
Screenshot evidence
Award notification showing a $500 bounty and $250 bonus. Program identity, account details, and weakness information are withheld. Open full image ↗
11 / AWARD NOTIFICATIONREDACTED DUE TO NDA
Confidential report · award and payment notification
Award acknowledged · Amount undisclosed
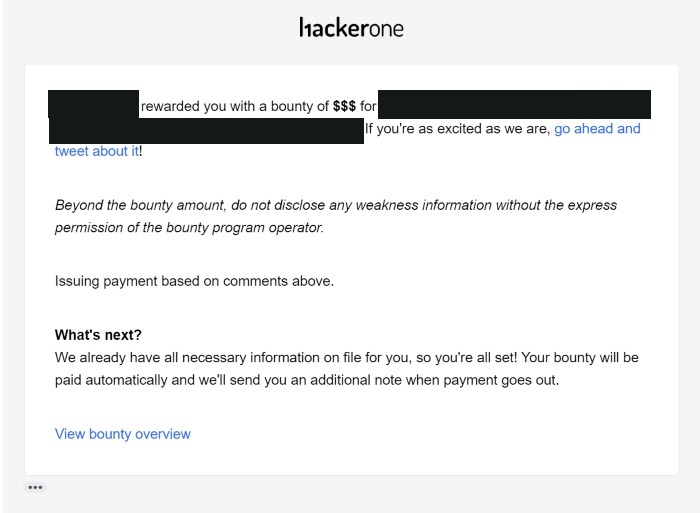
A HackerOne notification acknowledging an award and describing payment processing. The amount and technical details are not disclosed.
Read write-up & view evidence
Public record
The supplied HackerOne notification says a report was rewarded with a bounty. The amount appears as $$$ rather than a numeric value. This entry therefore records recognition without assigning or estimating a dollar amount.
Payment workflow
The message states that payment is being issued based on comments and that an additional note will follow when payment goes out. It also states that the necessary recipient information is already on file. These statements describe the notification workflow; the screenshot is not evidence of a completed bank transfer.
Confidential technical record
The program identity, report title, vulnerability classification, affected data, affected assets, and reproduction details are withheld in the published evidence. This entry does not expose the weakness information visible in the source image.
Evidence limits
No submission date, severity score, remediation state, or confirmed payment date is established by this capture. The notification is not assumed to correspond to another report on the page, and it is excluded from any earnings calculation.
Screenshot evidence
Notification showing an award acknowledgment and payment-processing text. The amount is represented as $$$ in the supplied screenshot; identifying and weakness details are obscured. Open full image ↗
12 / REPORT & REWARD RECORDREDACTED DUE TO NDA
Stored XSS · $1,500 listed
P2 · Unresolved · $1,500
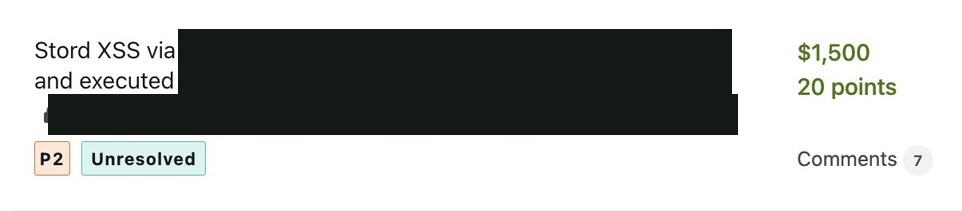
A stored cross-site scripting report showing $1,500, P2 priority, and unresolved status in the supplied report list.
Read write-up & view evidence
Reported issue
The visible title identifies stored cross-site scripting (XSS). The affected feature, stored input, rendering location, payload, and execution context are redacted due to NDA. The image is a report-list record rather than a technical proof-of-concept.
Recognition shown
The record displays $1,500 and 20 points. These are the values shown alongside this report in the supplied capture. The public evidence does not show a payment receipt, scoring rationale, or a breakdown of how the reward was determined.
Resolution state
The row is marked P2 and Unresolved. This entry preserves the unresolved state even though a monetary amount is visible. A displayed reward does not establish that the vulnerability was fixed.
Evidence handling and scope
This is the first of four separate rows in one supplied screenshot. Each row has its own cropped evidence image and write-up to keep its amount and status together. Program names, private identifiers, and technical details are obscured in the exported copy, with source metadata removed. The entries are not represented as newly verified or live report statuses.
Screenshot evidence
The first row of the supplied screenshot: stored XSS, $1,500, 20 points, P2, and Unresolved. Identifying and target-specific details are permanently obscured. Open full image ↗
13 / REPORT & REWARD RECORDREDACTED DUE TO NDA
Stored XSS · $1,300 listed
P2 · Unresolved · $1,300
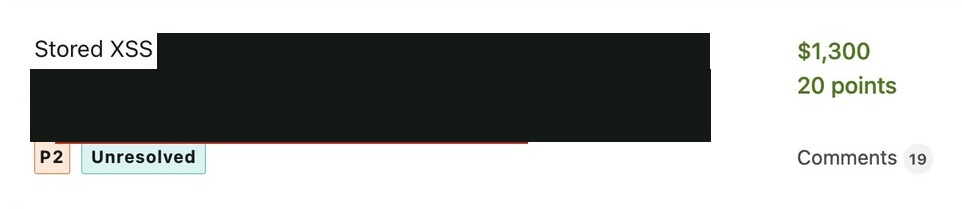
A stored cross-site scripting report showing $1,300, P2 priority, and unresolved status in the supplied report list.
Read write-up & view evidence
Reported issue
The visible title identifies stored cross-site scripting (XSS). The affected feature, stored input, rendering location, payload, and execution context are redacted due to NDA. The image is a report-list record rather than a technical proof-of-concept.
Recognition shown
The record displays $1,300 and 20 points. These are the values shown alongside this report in the supplied capture. The public evidence does not show a payment receipt, scoring rationale, or a breakdown of how the reward was determined.
Resolution state
The row is marked P2 and Unresolved. This entry preserves the unresolved state even though a monetary amount is visible. A displayed reward does not establish that the vulnerability was fixed.
Evidence handling and scope
This is the second of four separate rows in one supplied screenshot. Each row has its own cropped evidence image and write-up to keep its amount and status together. Program names, private identifiers, and technical details are obscured in the exported copy, with source metadata removed. The entries are not represented as newly verified or live report statuses.
Screenshot evidence
The second row of the supplied screenshot: stored XSS, $1,300, 20 points, P2, and Unresolved. Identifying and target-specific details are permanently obscured. Open full image ↗
14 / REPORT & REWARD RECORDREDACTED DUE TO NDA
Stored XSS · $500 listed
P3 · Unresolved · $500
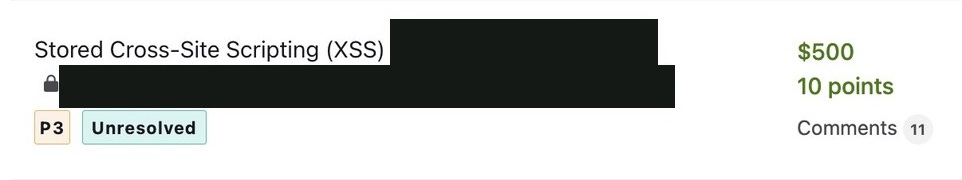
A stored cross-site scripting report showing $500, P3 priority, and unresolved status in the supplied report list.
Read write-up & view evidence
Reported issue
The visible title identifies stored cross-site scripting (XSS). The affected feature, stored input, rendering location, payload, and execution context are redacted due to NDA. The image is a report-list record rather than a technical proof-of-concept.
Recognition shown
The record displays $500 and 10 points. These are the values shown alongside this report in the supplied capture. The public evidence does not show a payment receipt, scoring rationale, or a breakdown of how the reward was determined.
Resolution state
The row is marked P3 and Unresolved. This entry preserves the unresolved state even though a monetary amount is visible. A displayed reward does not establish that the vulnerability was fixed.
Evidence handling and scope
This is the third of four separate rows in one supplied screenshot. Each row has its own cropped evidence image and write-up to keep its amount and status together. Program names, private identifiers, and technical details are obscured in the exported copy, with source metadata removed. The entries are not represented as newly verified or live report statuses.
Screenshot evidence
The third row of the supplied screenshot: stored XSS, $500, 10 points, P3, and Unresolved. Identifying and target-specific details are permanently obscured. Open full image ↗
15 / REPORT & REWARD RECORDREDACTED DUE TO NDA
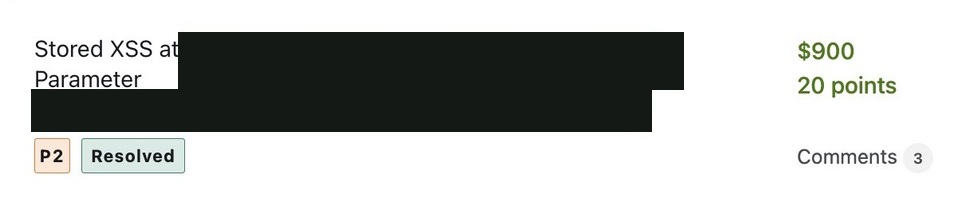
Stored XSS · $900 listed
P2 · Resolved · $900
A stored cross-site scripting report showing $900, P2 priority, and resolved status in the supplied report list.
Read write-up & view evidence
Reported issue
The visible title identifies stored cross-site scripting (XSS). The affected feature, stored input, rendering location, payload, and execution context are redacted due to NDA. The image is a report-list record rather than a technical proof-of-concept.
Recognition shown
The record displays $900 and 20 points. These are the values shown alongside this report in the supplied capture. The public evidence does not show a payment receipt, scoring rationale, or a breakdown of how the reward was determined.
Resolution state
The row is marked P2 and Resolved. This entry records the Resolved label shown in the screenshot. The fix details, resolution date, and independent retest results are not visible and are not inferred.
Evidence handling and scope
This is the fourth of four separate rows in one supplied screenshot. Each row has its own cropped evidence image and write-up to keep its amount and status together. Program names, private identifiers, and technical details are obscured in the exported copy, with source metadata removed. The entries are not represented as newly verified or live report statuses.
Screenshot evidence
The fourth row of the supplied screenshot: stored XSS, $900, 20 points, P2, and Resolved. Identifying and target-specific details are permanently obscured. Open full image ↗
Let’s talk security.
For professional opportunities and conversations about responsible security research.